
Solution · Executive Reporting
Executive-Level Reporting
Your board and executives want more visibility into third-party cyber risk. Panorays gives them a comprehensive view of your whole third-party portfolio and pinpoints potential regulatory and security gaps.
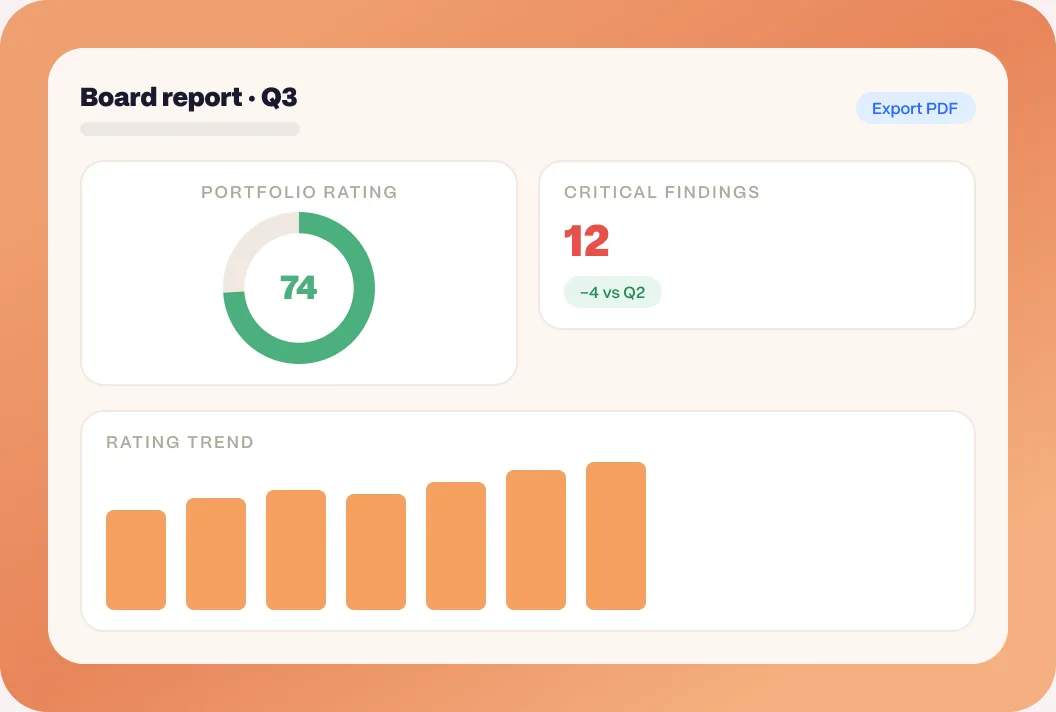
Clarity
Communicate Cyber Risk to Leaders
Panorays delivers reports leaders understand: your third-party security posture with suggested improvements, covering ratings analysis, regulatory compliance, fourth-party dependencies and critical findings, all customizable.
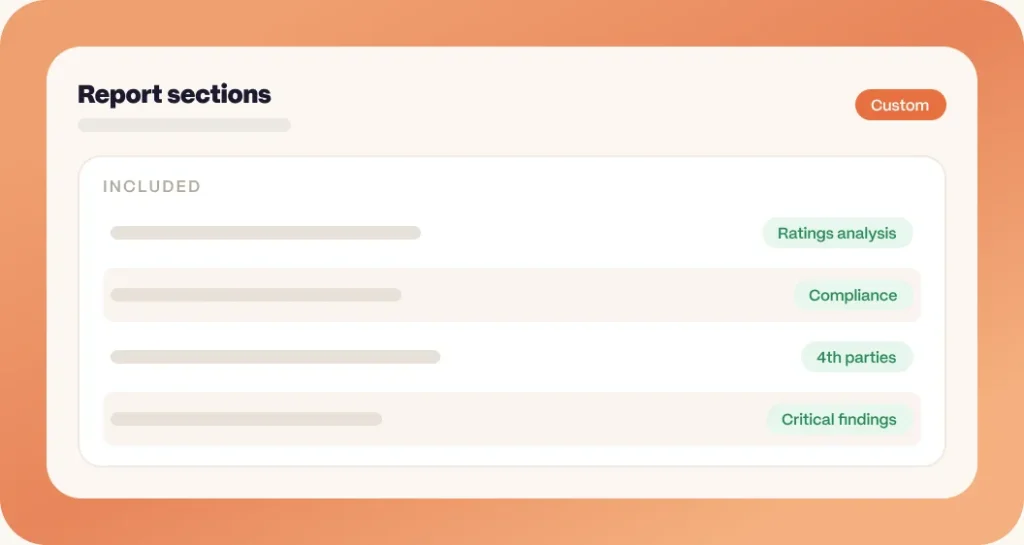
Decisions
Help Your Execs Make Informed Decisions
With clear visibility into your security challenges, board members and executives can identify and prioritize the areas that matter most.
Compliance
Comply with Regulations
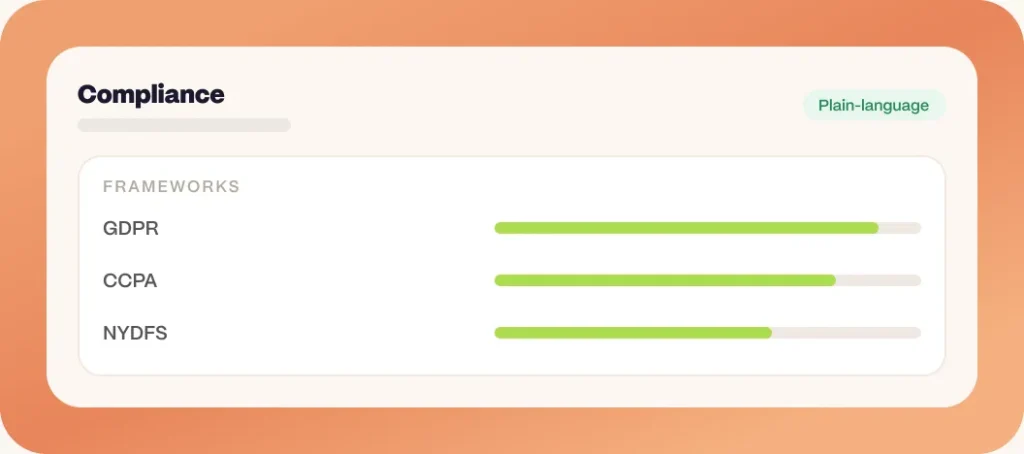
Holistic risk visibility helps leadership understand compliance requirements for you and your third parties under GDPR, CCPA and NYDFS, with metrics that non-security experts can read.
Demonstrate your compliance

PCI
AICPA SOC
ISO
GDPR
CCPA
Related Resources
 Guides
10 Key Questions to Include in Your Vendor Security Questionnaires
How to prioritze the most important supplier security questions.
 Guides
10 Essential Steps to NYDFS Compliance
Best practices for helping your third parties comply with nydfs.
 Webinars & Videos
Improving Third-Party Security Management: A Case Study with CAPTRUST
In today’s dynamic cyber world, third-party security is necessary, but can be challenging to implement. Learn how a leading investment firm succeeded…