
Third-Party Cyber Risk Management for Modern Supply Chains
Manage third-party and Nth-party risk from onboarding to remediation—with real-time visibility, context-based risk scoring, and automated remediation workflows. Panorays empowers organizations to take control of third-party risks with complete visibility.
- Reduce vendor onboarding time by 80%
- Deploy in days, not months
- Integrate with your existing security stack
- Scale across hundreds of vendors effortlessly
Trusted by Hundreds of Teams for Third-Party Cyber Risk Management
Onboarding at Scale
Panorays streamlines the onboarding process by detecting hidden Nth parties along your supply chain and automating the collection and verification of third-party documentation and assets. Within hours, Panorays makes it easy to detect, track, and assess hundreds of third parties at scale, while prioritizing them based on their criticality and business impact.
Comprehensive Risk Assessments
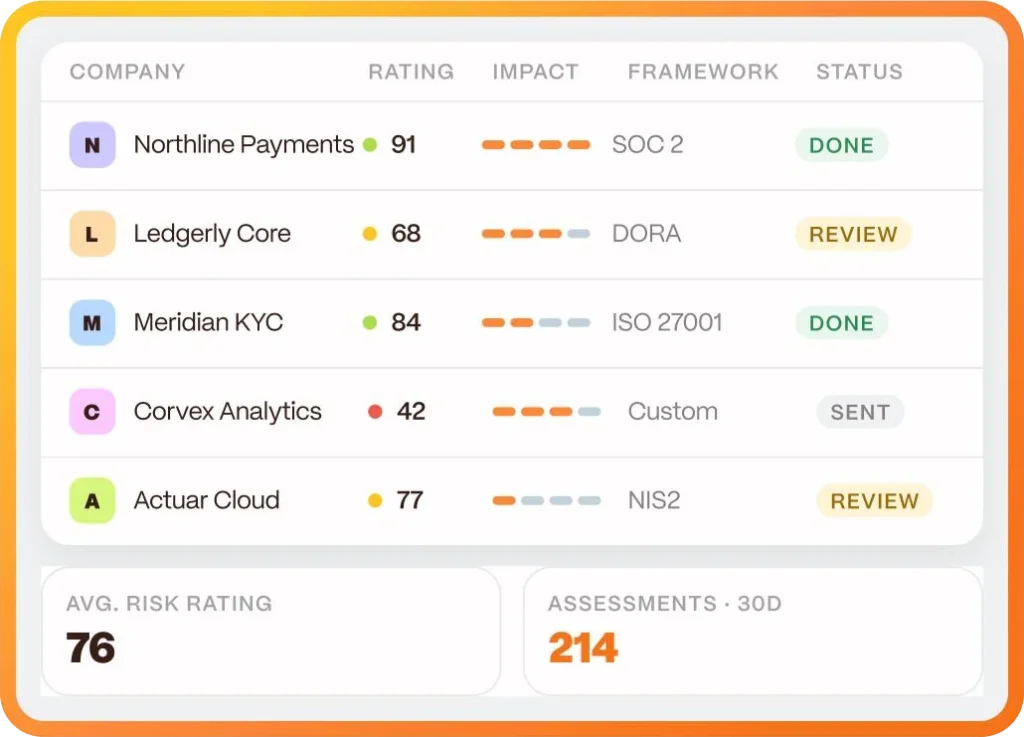
Panorays conducts detailed third-party risk assessments by analyzing cybersecurity posture against industry standards and regulations, providing detailed risk ratings and actionable insights to prioritize remediation efforts and manage threats across your supply chain.
Continuous Monitoring and Threat Detection
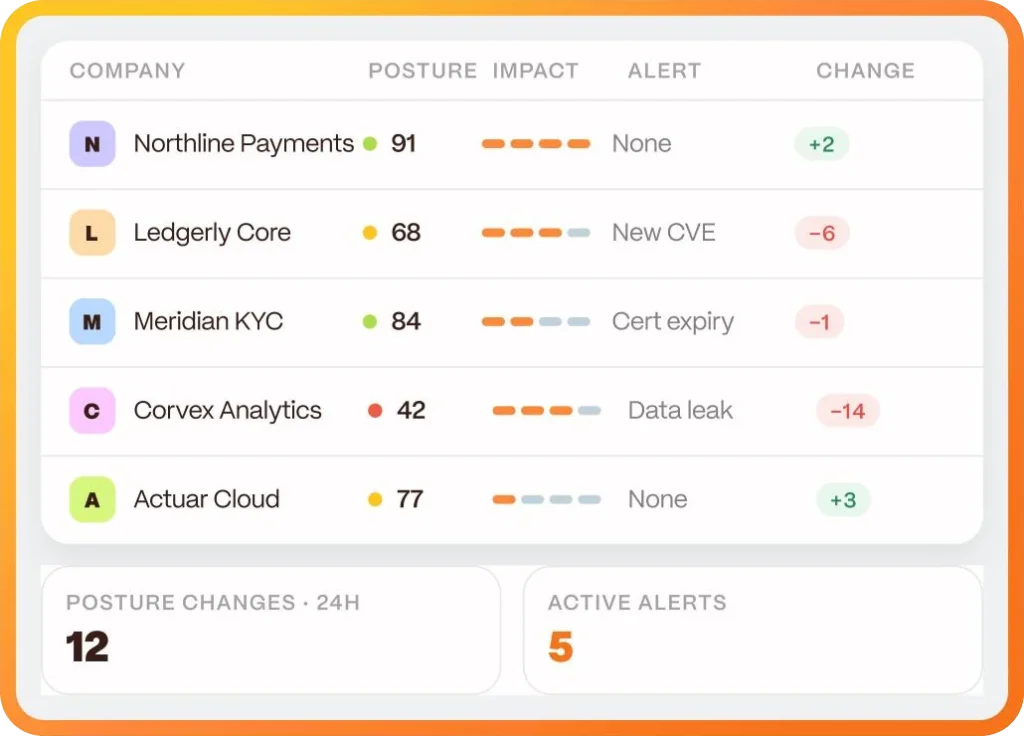
Continuously monitor changes in third-party security posture in real-time, leveraging automated alerts and threat intelligence to identify potential risks or vulnerabilities before they materialize.
Effortless Remediation and Collaboration
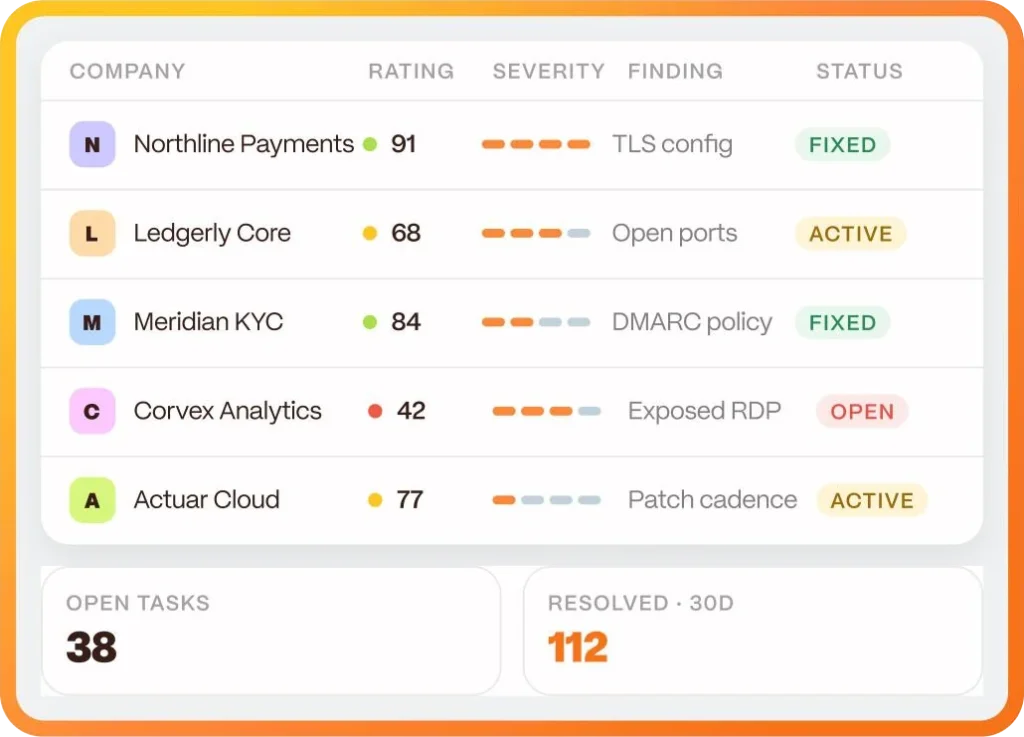
With auto-generated remediation plans, Panorays allows you to prioritize threats and work together with vendors to close security gaps. With centralized communication, documentation sharing, and progress tracking, Panorays ensures transparency and accountability throughout the vendor lifecycle.
Why Security Teams Choose Panorays
Prioritized, Context-Based Third-Party Risk Management
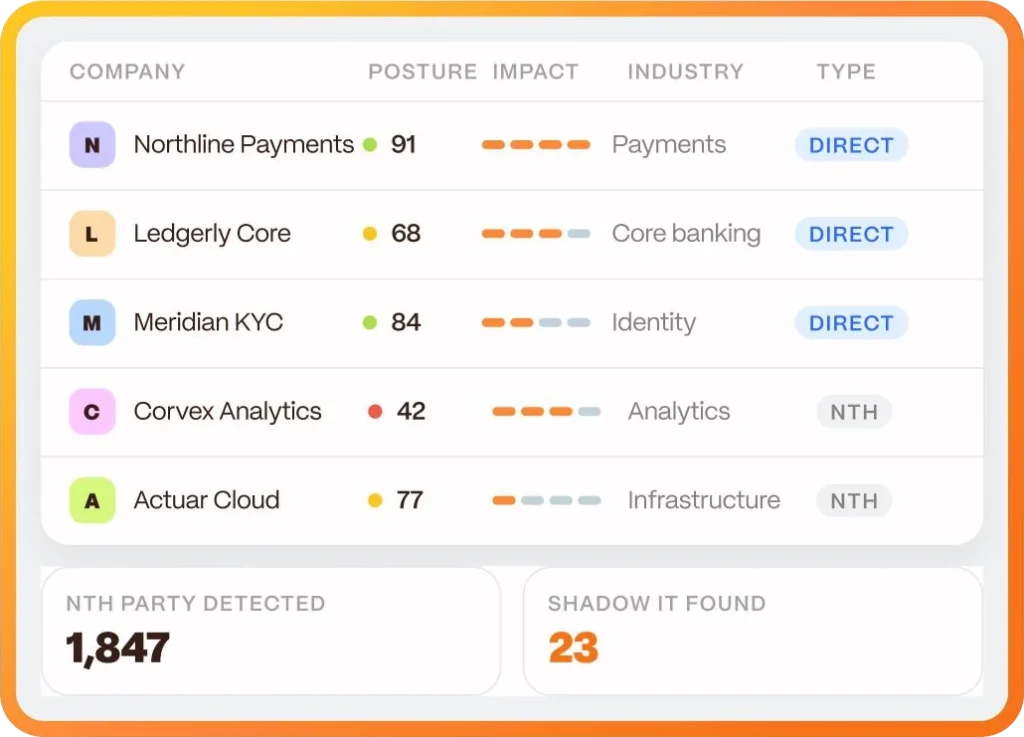
Identify Supply Chain Risks
Panorays’ enhanced Supply Chain Detection discovers 3rd-Nth parties along your supply chain, uncovering hidden risks and exposing Shadow IT. Review hundreds of vendors and add the most critical ones for close monitoring and assessment.
The Essentials You Need for Comprehensive Third-Party Cyber Risk Management
FAQ
Third-Party Cyber Risk Management Frequently Asked Questions
What is third-party cyber risk management?
Third-party cyber risk management involves identifying, assessing, and remediating potential cybersecurity threats and vulnerabilities posed by external entities such as vendors, suppliers, or partners that are a part of an organization’s digital landscape.
Why is third-party cyber risk management important?
Third-party cyber risk management is crucial because it helps organizations protect themselves from security breaches, data leaks, and other cyber threats that could originate from their relationships with external parties, safeguarding sensitive information and preserving trust with customers and stakeholders.
What degree of third-party cyber risk management do you need?
The degree of third-party cyber risk management needed varies depending on factors such as the sensitivity of the data shared with external parties, the potential impact of a security breach, and the regulatory requirements applicable to the organization’s industry. A thorough risk assessment can help determine the appropriate level of management needed.
How do you select a third-party cyber risk management framework?
When selecting a third-party cyber risk management framework, consider factors such as its alignment with industry standards, the comprehensiveness of its risk assessment methodologies, its scalability to accommodate the organization’s needs, and its ability to facilitate ongoing monitoring and mitigation of cyber risks posed by external entities. Additionally, assess its compatibility with existing cybersecurity practices and technologies within the organization.
How is Panorays different from other third-party risk management solutions?
Panorays goes beyond traditional vendor risk management by providing full visibility into both third- and Nth-party risk. Unlike point-in-time assessment tools, it combines automated security questionnaires with continuous external monitoring to deliver a complete, real-time view of vendor risk. With context-based risk scoring and built-in remediation workflows, security teams can prioritize what matters most and take action quickly.
How long does it take to onboard vendors with Panorays?
Panorays enables organizations to onboard vendors in hours, not weeks. The platform automates data collection, identifies vendor assets, and uncovers hidden dependencies, allowing security teams to assess and prioritize vendors quickly without manual back-and-forth.
Can Panorays manage large and complex vendor ecosystems?
Yes. Panorays is designed to scale across hundreds or thousands of vendors. With automated onboarding, risk prioritization, and continuous monitoring, organizations can efficiently manage complex supply chains without increasing operational overhead.
Does Panorays integrate with existing security tools?
Panorays integrates with existing security and IT systems, allowing organizations to incorporate third-party risk management into their broader security stack. This ensures seamless workflows, centralized visibility, and better alignment between internal and external risk management processes.
How does Panorays monitor third-party risk continuously?
Panorays continuously monitors vendors by analyzing their external attack surface, threat intelligence signals, and security posture changes in real time. Automated alerts notify organizations of emerging risks, enabling them to respond proactively rather than relying on periodic assessments.
Which frameworks and regulations does Panorays support?
Panorays supports leading cybersecurity frameworks and regulations, including NIST CSF, ISO 27001, SOC 2, DORA, NIS2, and more. The platform helps organizations align third-party risk management processes with these standards through structured assessments, continuous monitoring, and remediation tracking.
What is Nth-party risk, and why does it matter?
Nth-party risk refers to risks introduced by your vendors’ vendors; third parties beyond your direct suppliers. These hidden dependencies can create blind spots in your supply chain and increase exposure to cyber threats. Managing Nth-party risk is essential for gaining full visibility and ensuring resilience across your extended vendor ecosystem.
So do we click?
See how Panorays takes control of third-party cyber risk from onboarding to remediation.