
Solution · DORA Compliance
Achieve DORA Compliance with Confidence
Get ready for the Digital Operational Resilience Act in 2025 and secure your organization’s digital supply chain with Panorays.
Trusted by Hundreds of Teams for Third-Party Cyber Risk Management
Navigate DORA With Ease
All You Need to Master DORA Compliance
Categorize
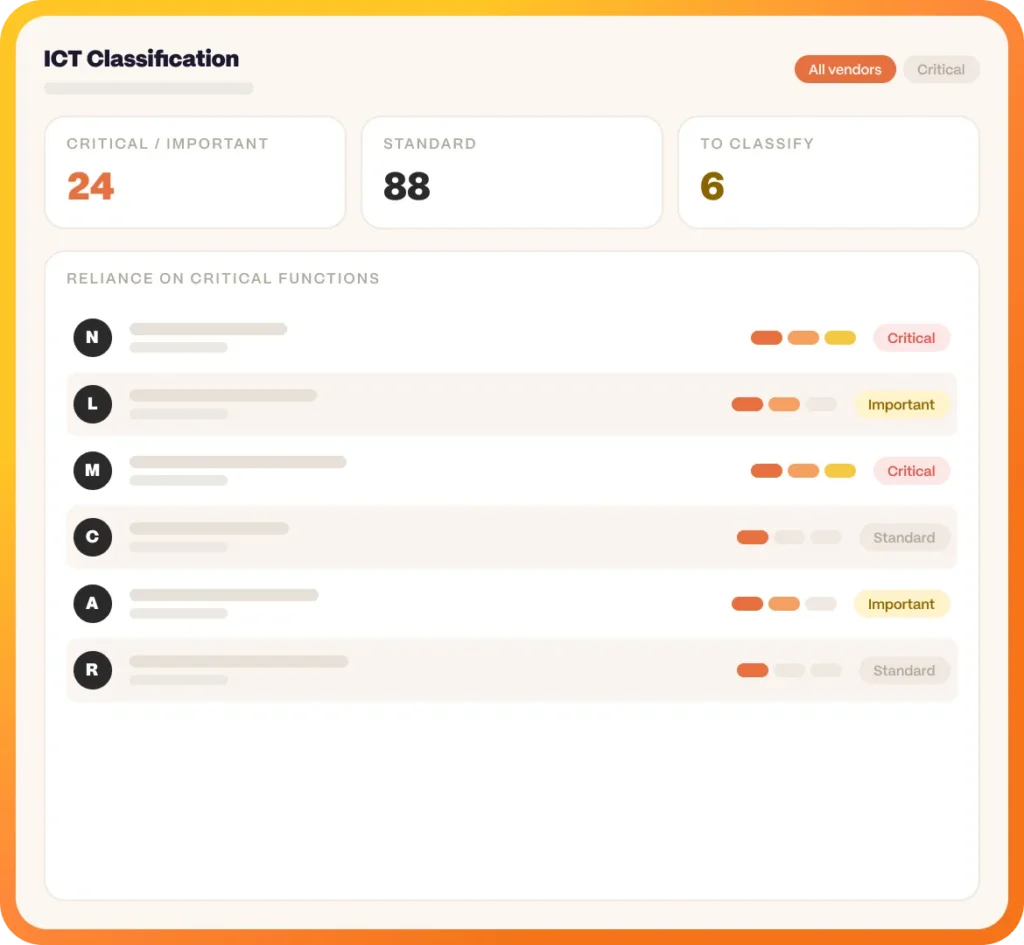
Categorize Third-Party ICTs
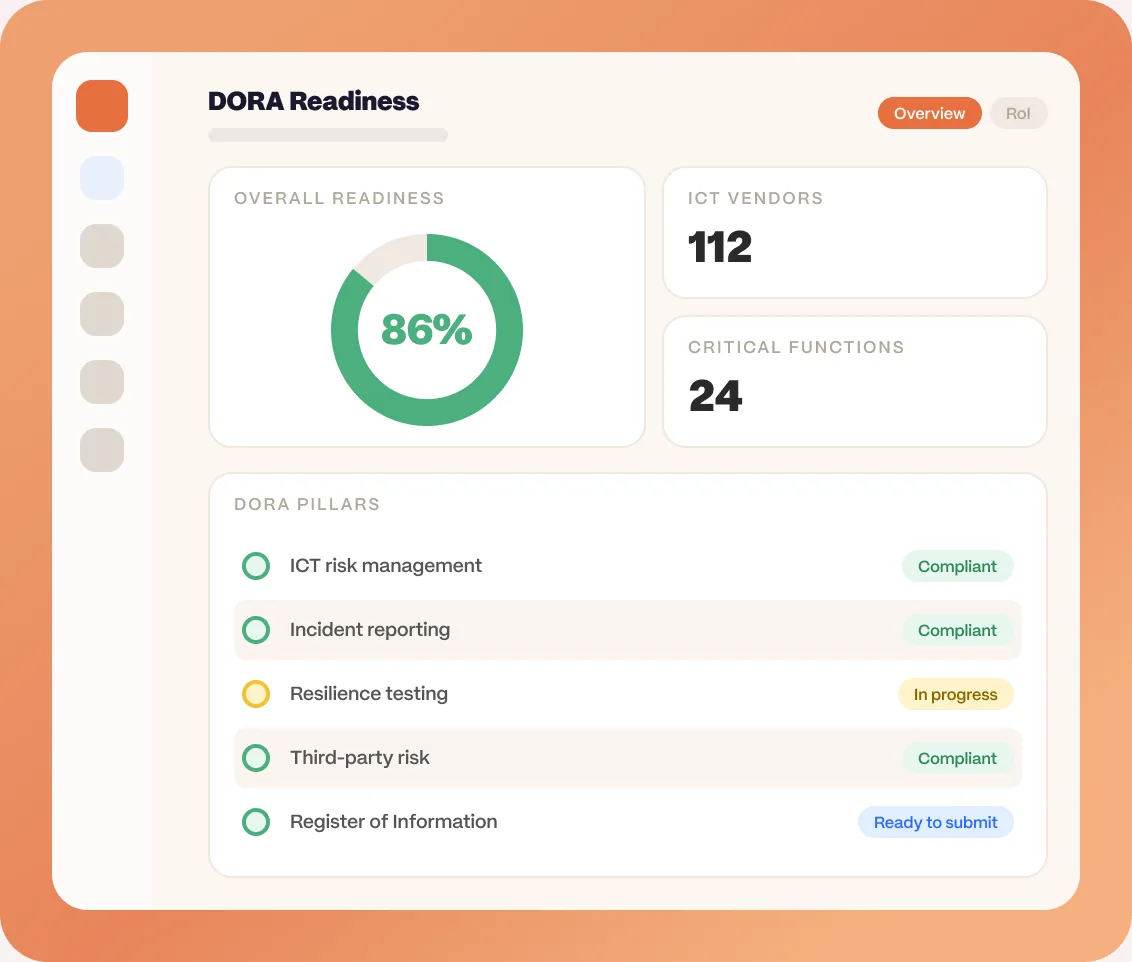
With DORA-specific classification questionnaires, Panorays sorts your ICT vendors based on the level of reliance on critical functions.
FAQ
DORA Compliance FAQs
What is the Digital Operational Resilience Act (DORA)?
DORA is a landmark EU regulation designed to harmonize IT security requirements across the financial sector. Unlike previous frameworks that focused primarily on capital reserves, DORA mandates that banks, insurers, and investment firms prove they can withstand, respond to, and recover from all types of ICT-related disruptions. It elevates third-party risk management from a “best practice” to a mandatory board-level accountability.
When did DORA go into effect?
DORA officially entered into force on January 16, 2023. The implementation window has now closed, with the legal compliance deadline having passed on January 17, 2025. Regulators are now actively enforcing these standards; as of Spring 2026, financial entities are required to submit their finalized Register of Information (RoI) to face rigorous Data Quality audits by European Supervisory Authorities.
Who needs to comply with DORA?
The scope of DORA is vast, covering over 20 different types of financial entities including credit institutions, payment providers, crypto-asset service providers, and insurance undertakings. Crucially, it also applies to “critical” ICT third-party service providers, meaning tech companies that provide essential infrastructure to the financial sector are now directly under regulatory oversight.
How can organizations improve operational resilience under DORA?
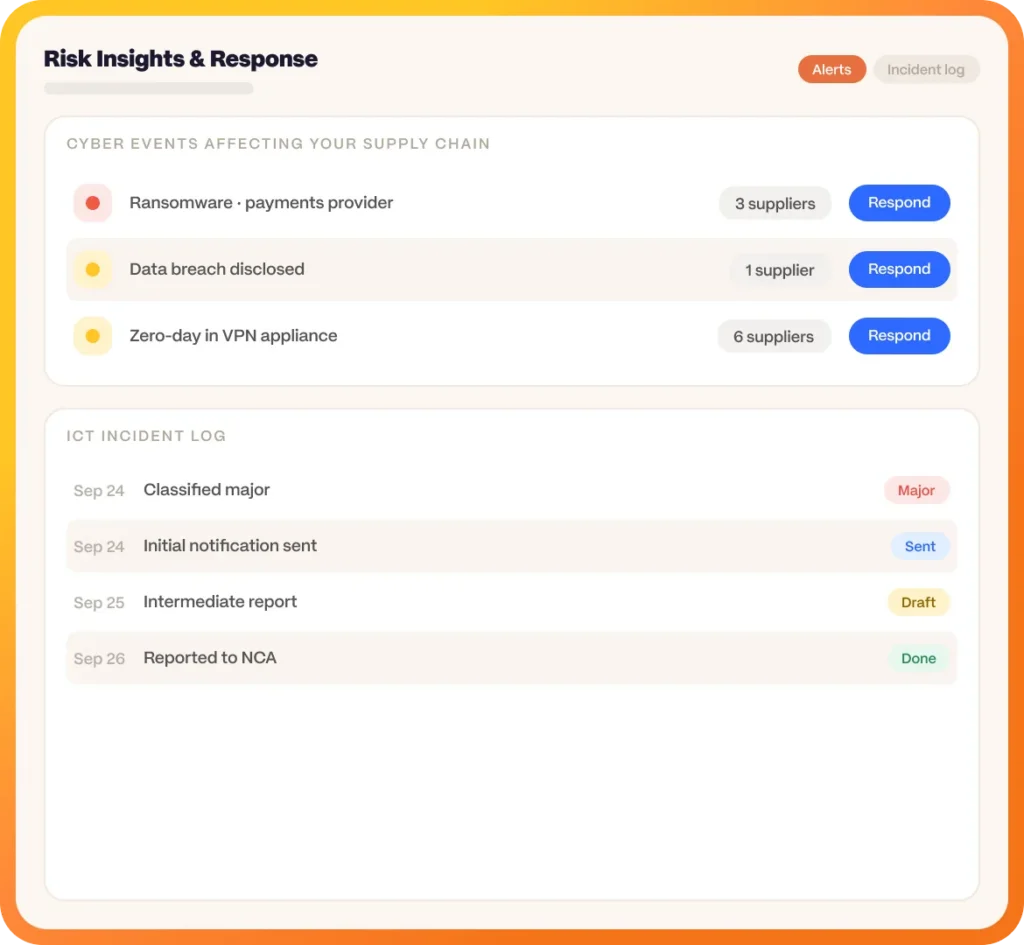
True resilience requires moving from static, point-in-time assessments to a dynamic “Risk DNA” approach. Organizations improve resilience by implementing continuous monitoring of their ICT environment, establishing robust incident response playbooks, conducting regular threat-led penetration testing (TLPT), and ensuring deep visibility into their broader digital supply chain.
How does Panorays support DORA compliance?
Panorays automates the most labor-intensive pillars of DORA. We provide a centralized platform to manage the entire ICT third-party lifecycle, from initial risk-based onboarding and DORA-specific assessments to continuous monitoring and the generation of the mandatory Register of Information. Our AI-driven insights ensure that your compliance data is accurate, defensible, and actionable.
Why is digital supply chain visibility important for DORA compliance?
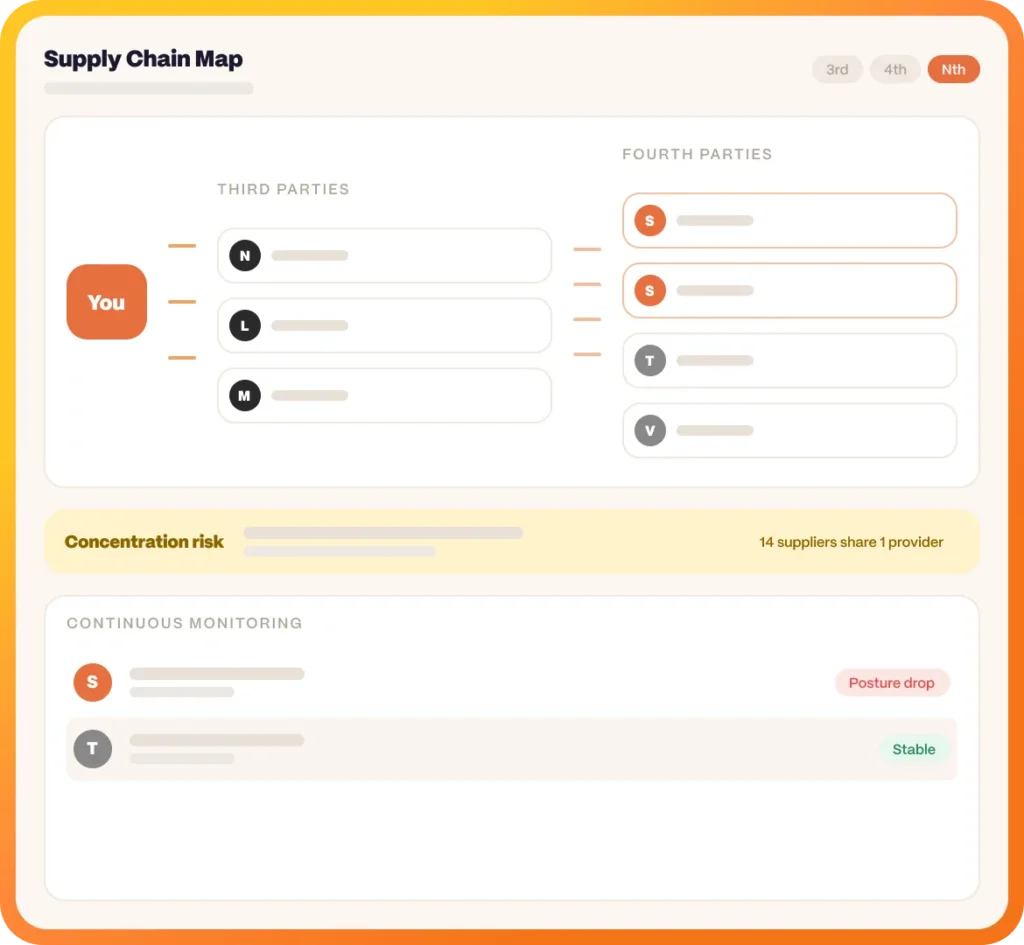
Under DORA, you are responsible for the resilience of your entire supply chain, including Nth-party providers. If a subcontractor deep in your supply chain fails, it can compromise your critical functions. Panorays provides the visibility needed to map these indirect relationships, allowing you to manage concentration risk and ensure that your vendors’ vendors meet your security standards.
What is a DORA Register of Information (RoI)?
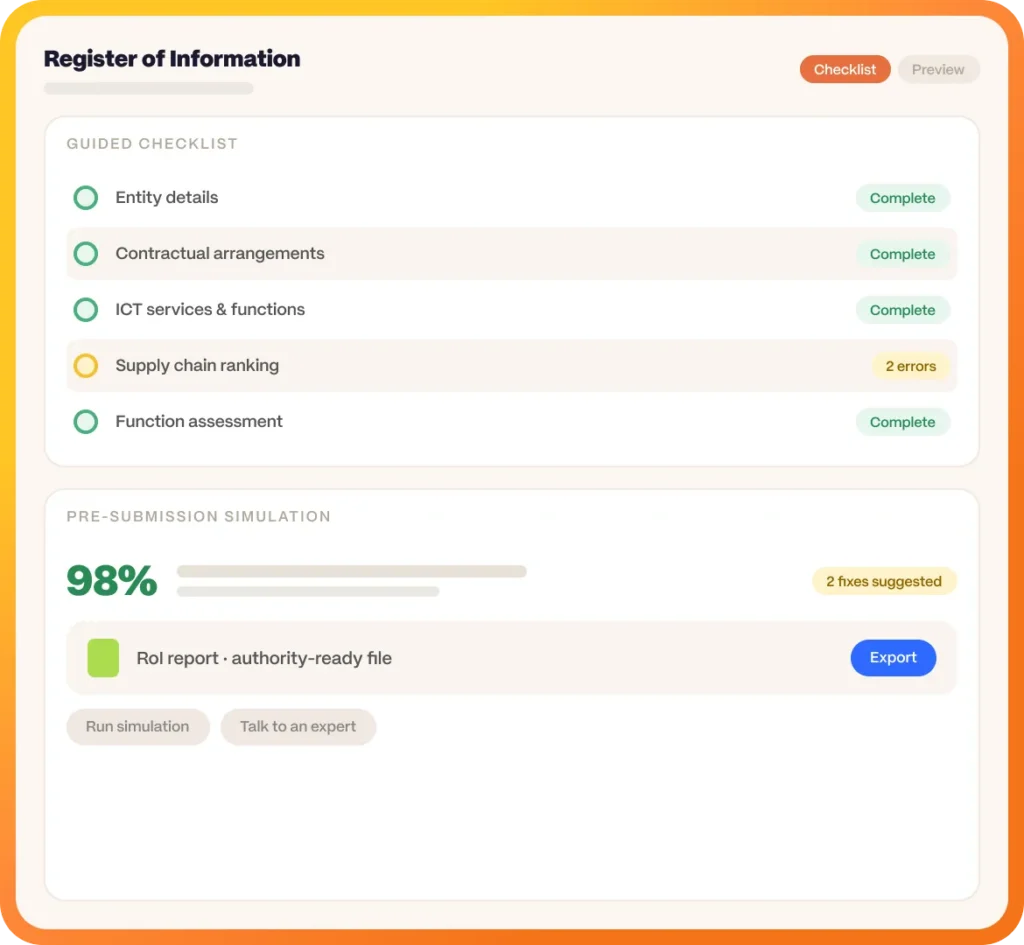
The Register of Information is a mandatory, standardized record of all contractual arrangements with ICT third-party providers. It must be maintained at individual and consolidated levels and be ready for submission to National Competent Authorities (NCAs) upon request. Panorays automates the collection of this data, providing a single source of truth that is always audit-ready.
What does DORA require for ICT third-party risk management?
DORA mandates a holistic approach to third-party risk. This includes performing rigorous due diligence before entering contracts, ensuring all ICT contracts include specific clauses (like audit rights and exit strategies), and continuously monitoring vendor performance. It also requires organizations to assess the “potential systemic risk” posed by a heavy reliance on a single provider.
How can organizations prepare for DORA compliance?
Preparation should begin with a gap analysis of your current ICT risk framework. Key steps include mapping your ICT supply chain, identifying “Critical or Important Functions,” updating vendor contracts to meet Article 30 requirements, and implementing an automated TPCRM platform like Panorays to handle the ongoing burden of monitoring and reporting.
How does AI help streamline DORA compliance workflows?
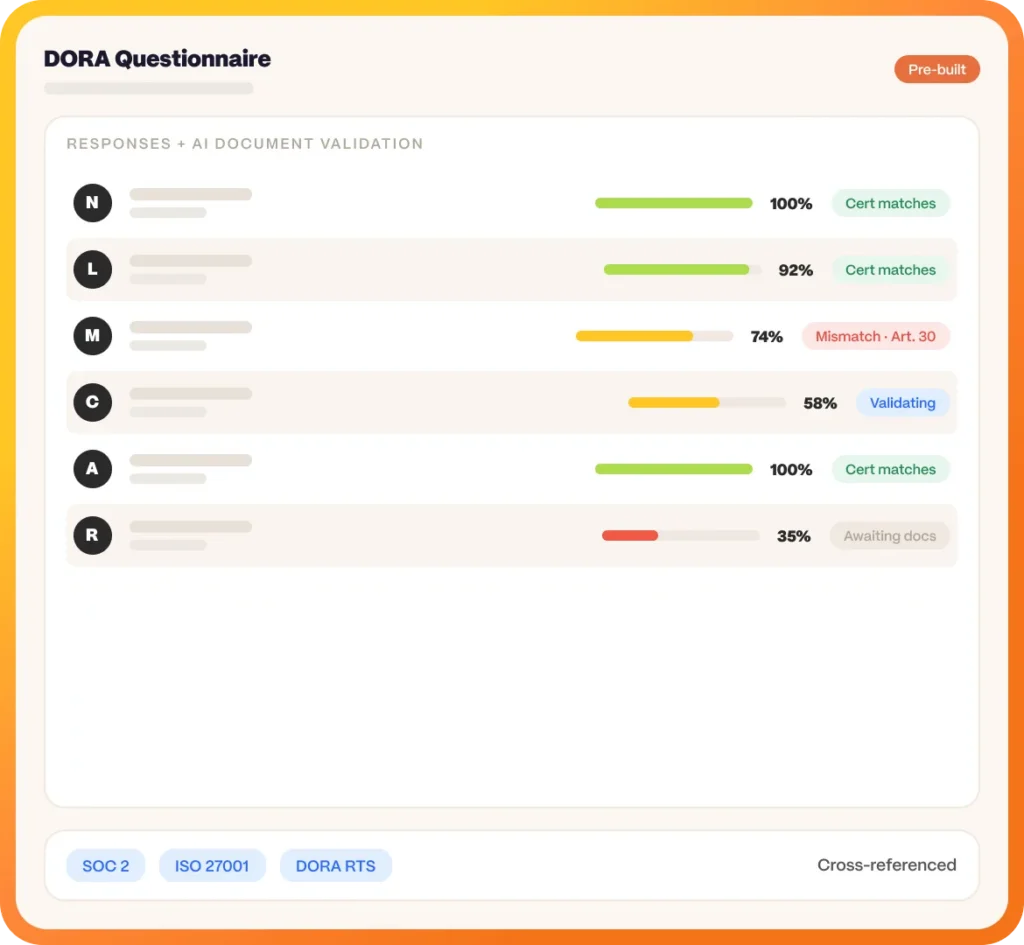
AI acts as a force multiplier for overstretched compliance teams. In Panorays, AI is used to automatically validate vendor evidence, ensuring that uploaded certifications match questionnaire responses. This reduces manual review time by up to 80% and provides a much higher level of accuracy during the “early error handling” phase of building your Register of Information.
How does DORA relate to third-party cyber risk management?
Third-party risk is not just a part of DORA, it is a central pillar. DORA recognizes that the financial sector’s resilience is only as strong as its weakest link. Therefore, the regulation treats third-party cyber risk management (TPCRM) as a core operational requirement, demanding the same level of security and oversight for your vendors as you apply to your own internal systems.
Can DORA compliance processes be automated?
Automation is essential for DORA compliance at scale. Manually tracking hundreds of ICT vendors, monitoring their real-time cyber posture, and maintaining an up-to-date Register of Information is nearly impossible without automation. Panorays enables you to automate the entire workflow, allowing your team to focus on resolving actual risks rather than chasing paperwork.
How does DORA impact financial institutions?
DORA fundamentally changes the CISO and Risk Manager’s role by making ICT resilience a legal mandate. It requires a cultural shift toward transparency and proactive defense. Institutions must now be able to prove, with data, that they have a complete handle on their digital supply chain and can maintain service continuity even during a major cyber event.
What are the penalties for non-compliance with DORA?
The stakes are high. Beyond the reputational damage of a public failure, regulators can impose significant administrative fines. For critical ICT providers, NCAs can levy “periodic penalty payments” of up to 1% of the average daily worldwide turnover. For financial entities, fines are determined by national laws but are designed to be “effective, proportionate, and dissuasive.”