
Platform · Attack Surface
External Attack Surface Management
Gain continuous visibility into your external attack surface and your vendors’ digital footprint. Panorays helps security teams identify exposed assets, uncover third- and Nth-party risks, and prioritize remediation before attackers can exploit vulnerabilities.
Leading Organizations Use Panorays to Secure Their Third-Party Ecosystem
Accuracy at our core
External Attack Surface Monitoring for Third-Party Cyber Risk
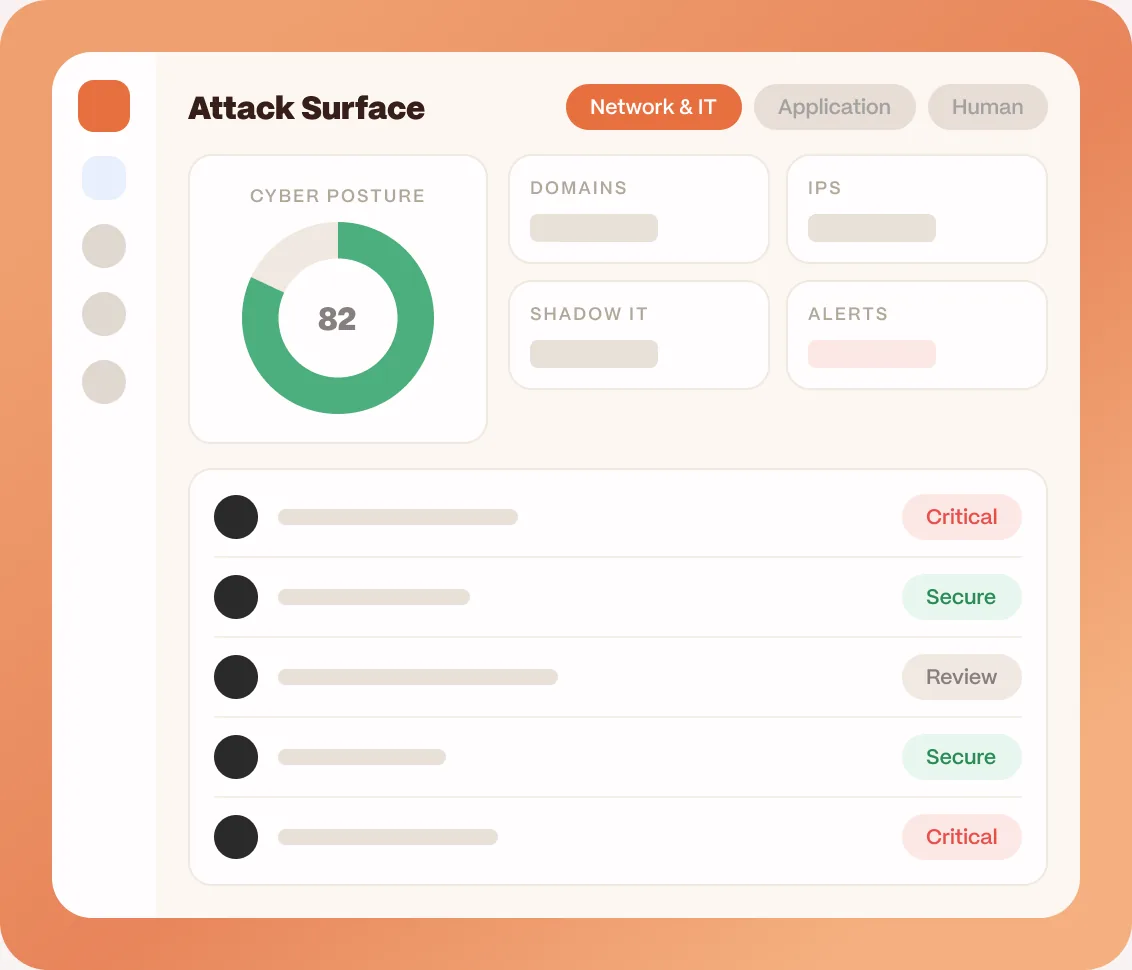
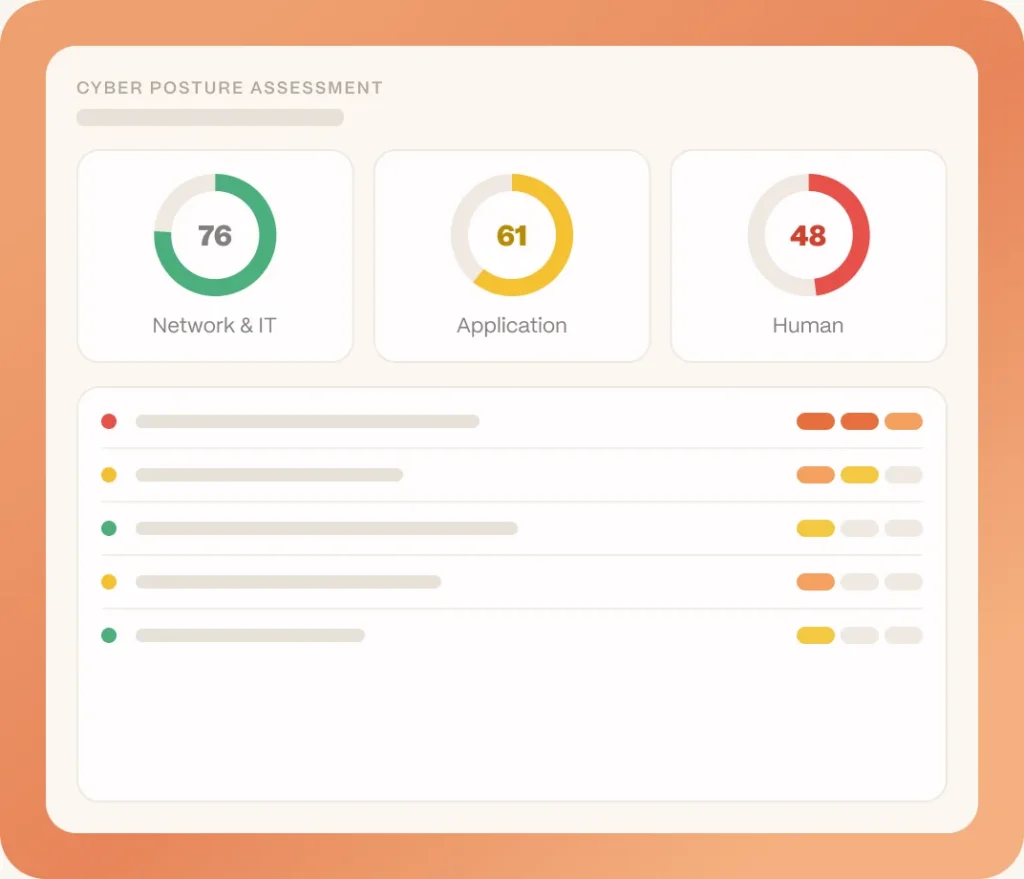
Panorays’ industry-leading technology scans thousands of assets across your supply chain, with real-time, accurate, and reliable data, so you can confidently evaluate your third-party cyber risks. Our detailed Cyber Posture Assessments uncover vulnerabilities and identify potential security gaps with a complete breakdown of your security posture as well as that of your third parties.
Insights beyond the surface
External Attack Surface Insights
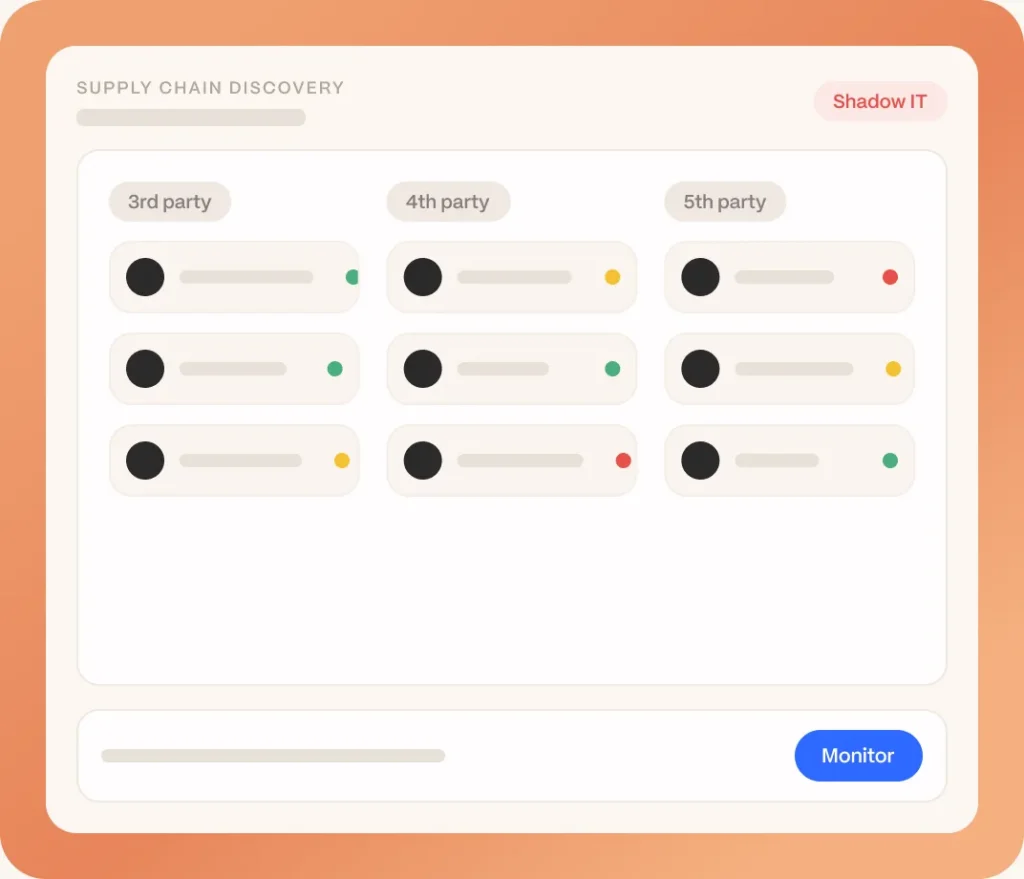
Our Attack Surface Management tools let you drill deep into your supply chain risks by revealing Shadow IT and discovering 4th and 5th parties. You can easily assess the cyber posture of indirect parties and select critical vendors for continuous monitoring, so you can be the first to know of risks across your supply chain.
Risk Insights Portal
Real-Time Data on Evolving Risks
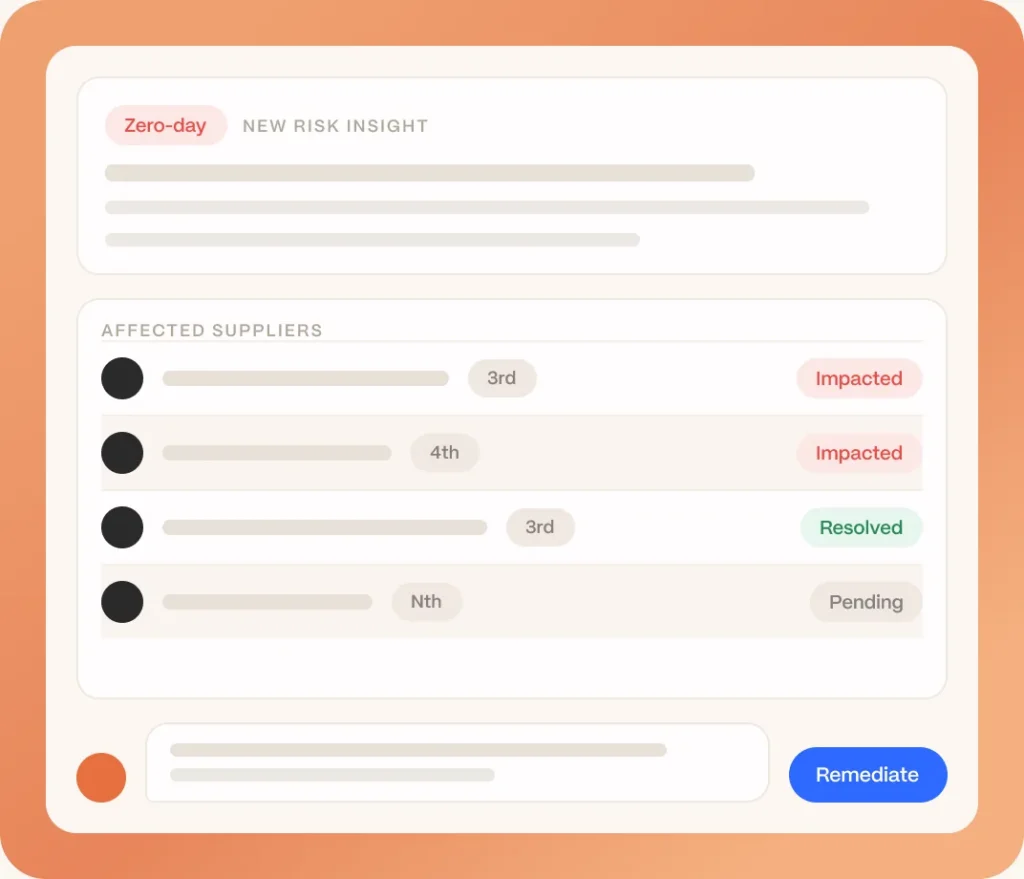
Panorays’ unique Risk Insights Portal gives you instant alerts on cybersecurity threats such as breaches, vulnerabilities, and zero-day attacks, with a detailed analysis of their impact on your direct and indirect suppliers. Panorays’ in-platform communication makes it easy to resolve vulnerabilities and remediate critical findings, all with a clear audit trail.
Manage Your External Attack Surface and Reduce Cyber Risk
Comprehensive Asset Management and Discovery
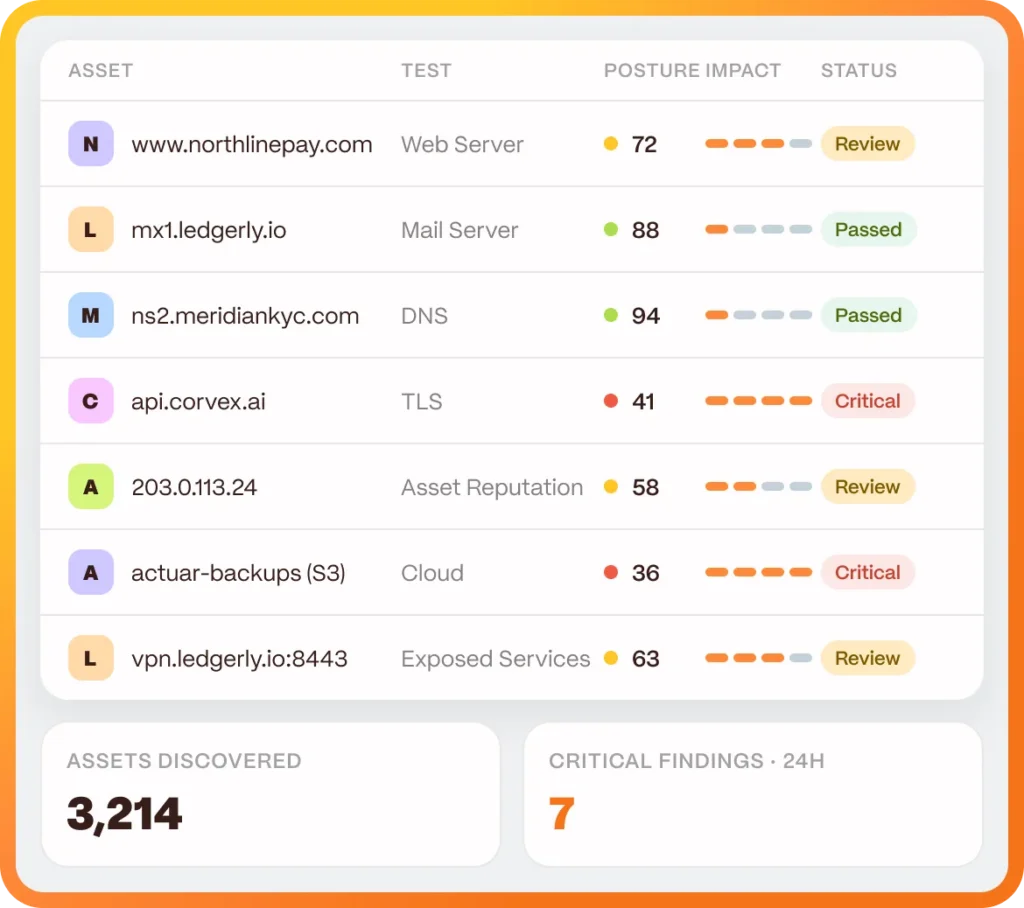
Panorays performs hundreds of tests across your attack surface, collecting information on exposed assets so you can understand potential risks across three layers.
Layer 1 of 3 · 7 subcategories
Network & IT
The external-facing network infrastructure and services.
- Web Server — outdated software, misconfigurations and missing security headers.
- Mail Server — mail servers and email security records like SPF, DKIM and DMARC.
- DNS — DNS records and configuration weaknesses attackers can abuse.
- TLS — certificates, protocols and encryption strength.
- Asset Reputation — assets on blocklists or linked to malicious activity.
- Cloud — exposed storage and misconfigured cloud-hosted assets.
- Exposed Services — open ports and services that shouldn’t be public.
Holistic Attack Surface Management
FAQ
External Attack Surface Frequently Asked Questions
How does Panorays monitor vendor security posture?
Panorays provides non-intrusive, continuous visibility into your third-party ecosystem by automatically scanning and mapping thousands of external-facing digital assets across your supply chain. It performs hundreds of automated tests across network, application, and human layers to deliver real-time Cyber Posture Assessments and dynamic risk ratings, alerting you instantly to new vulnerabilities, breaches, or zero-day threats.
What is external attack surface management?
External attack surface management involves monitoring and managing the digital assets and entry points that are accessible from outside an organization’s network. EASM focuses on protecting the organization from external threats and vulnerabilities.
How does continuous attack surface monitoring work?
Continuous monitoring works by utilizing automated scanning tools that scout the internet 24/7 to discover, track, and analyze an organization’s (and its vendors’) external digital footprint. Instead of relying on a point-in-time snapshot, it constantly checks for new asset exposures, misconfigurations, shadow IT, or dark web mentions, triggering real-time alerts the moment a security change or potential risk is detected.
What are the benefits of attack surface monitoring?
Attack surface monitoring lets you identify vulnerabilities and discover potential weaknesses in your digital assets. It also aids in cyber risk reduction and improved security posture, enabling proactive risk mitigation by addressing vulnerabilities before they are exploited.
What is the difference between internal and external attack surface management?
External Attack Surface Management (EASM) focuses on identifying and securing internet-facing assets (such as public domains, cloud misconfigurations, exposed servers, and third-party supply chain risks) that are visible to outside attackers. Internal Attack Surface Management deals with threats inside the perimeter, focusing on lateral movement, internal network permissions, endpoint security, and vulnerabilities accessible only to those who already have access to the internal network.
What are the different types of attack surfaces?
- Network attack surface: The external-facing network infrastructure and services.
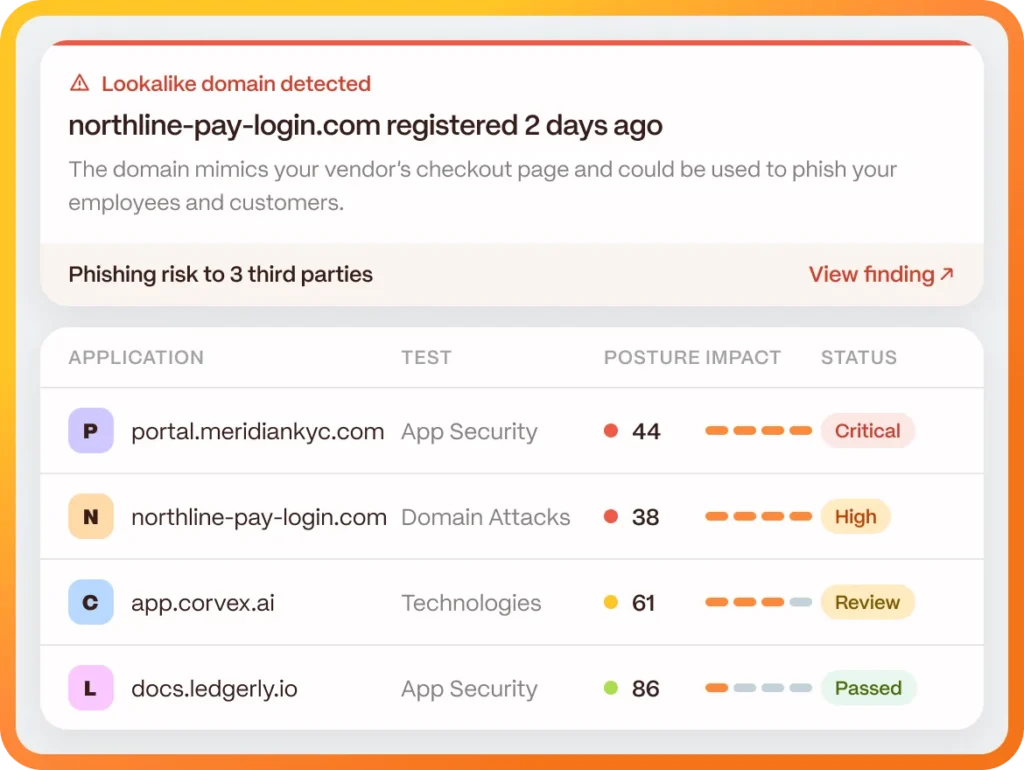
- Application attack surface: The software applications and web services exposed to potential attacks.
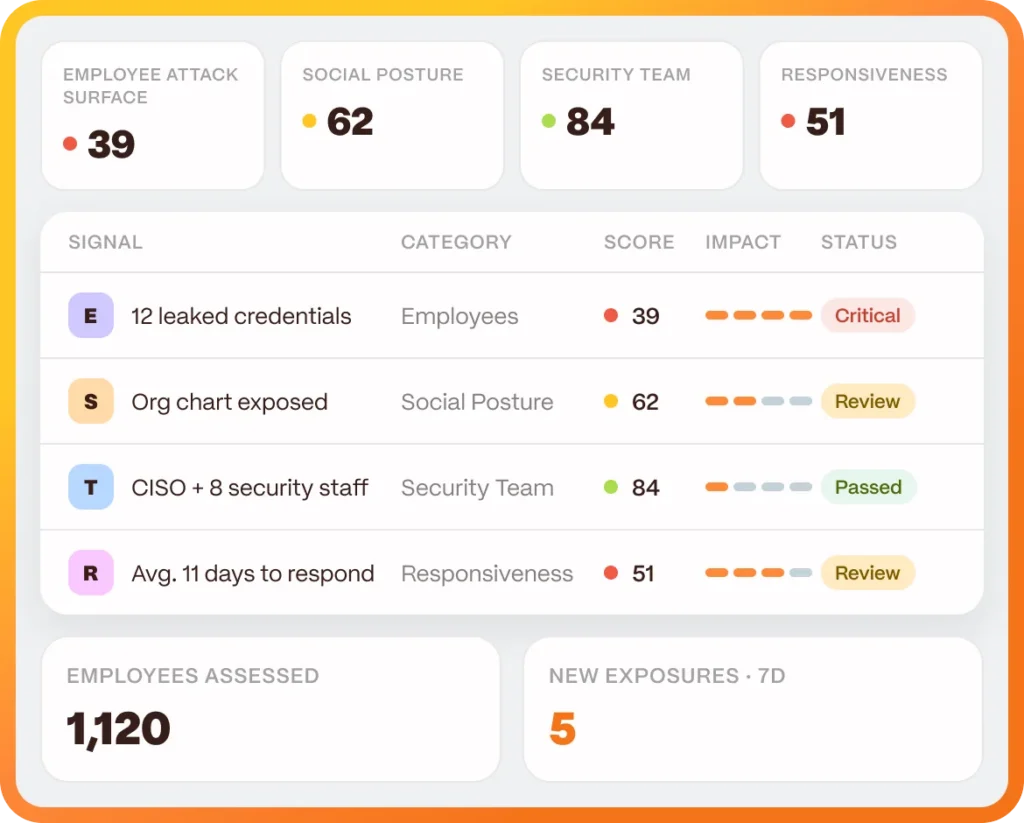
- Human attack surface: The vulnerabilities related to employees, their behaviors, and access privileges.
- Supply chain attack surface: The risks associated with third-party vendors and partners.
What is the attack surface process?
- Identification: Identifying all assets, entry points, and potential vulnerabilities.
- Assessment: Analyzing the identified elements for weaknesses and risks.
- Mitigation: Implementing security measures to reduce the attack surface.
- Monitoring: Continuously observing and updating the attack surface based on changes and emerging threats.
How do you deploy attack surface reduction?
To reduce your external attack surface, it is recommended to implement access controls and limit unnecessary access to resources, undergo patch management, network segmentation, and application security, along with training employees in security best practices.
How is the attack surface measured?
An attack surface is measured by quantifying the total volume and severity of exposed digital assets and potential entry points. Key metrics include the number of active external-facing IPs, domains, and cloud resources, alongside routine vulnerability assessments and attack surface mapping. Tracking how these metrics, risk ratings, and remediation response times change over time provides a comprehensive baseline for measuring your security posture.
What is shadow IT, and why is it risky?
Shadow IT refers to any software, hardware, cloud service, or application used within an organization without the explicit approval or oversight of the IT and security teams. It is inherently risky because these unmanaged assets bypass standard security protocols, patch schedules, and compliance checks, leaving open vulnerabilities that attackers can easily discover and exploit to gain entry into the corporate network.